9
October, 2026
How Embedded Systems in Aerospace Improve Aircraft Performance and Reliability
An aircraft may carry a faster processor and collect more sensor data without becoming more reliable. The improvement comes from how that computing capacity is used: controlling an engine, responding to a flight command, or detecting a developing fault.
Embedded systems in aerospace connect these functions to the aircraft’s physical behavior. Their design determines whether better computing delivers better control, fewer disruptions, and useful maintenance information.
Where Aircraft Embedded Systems Influence Performance
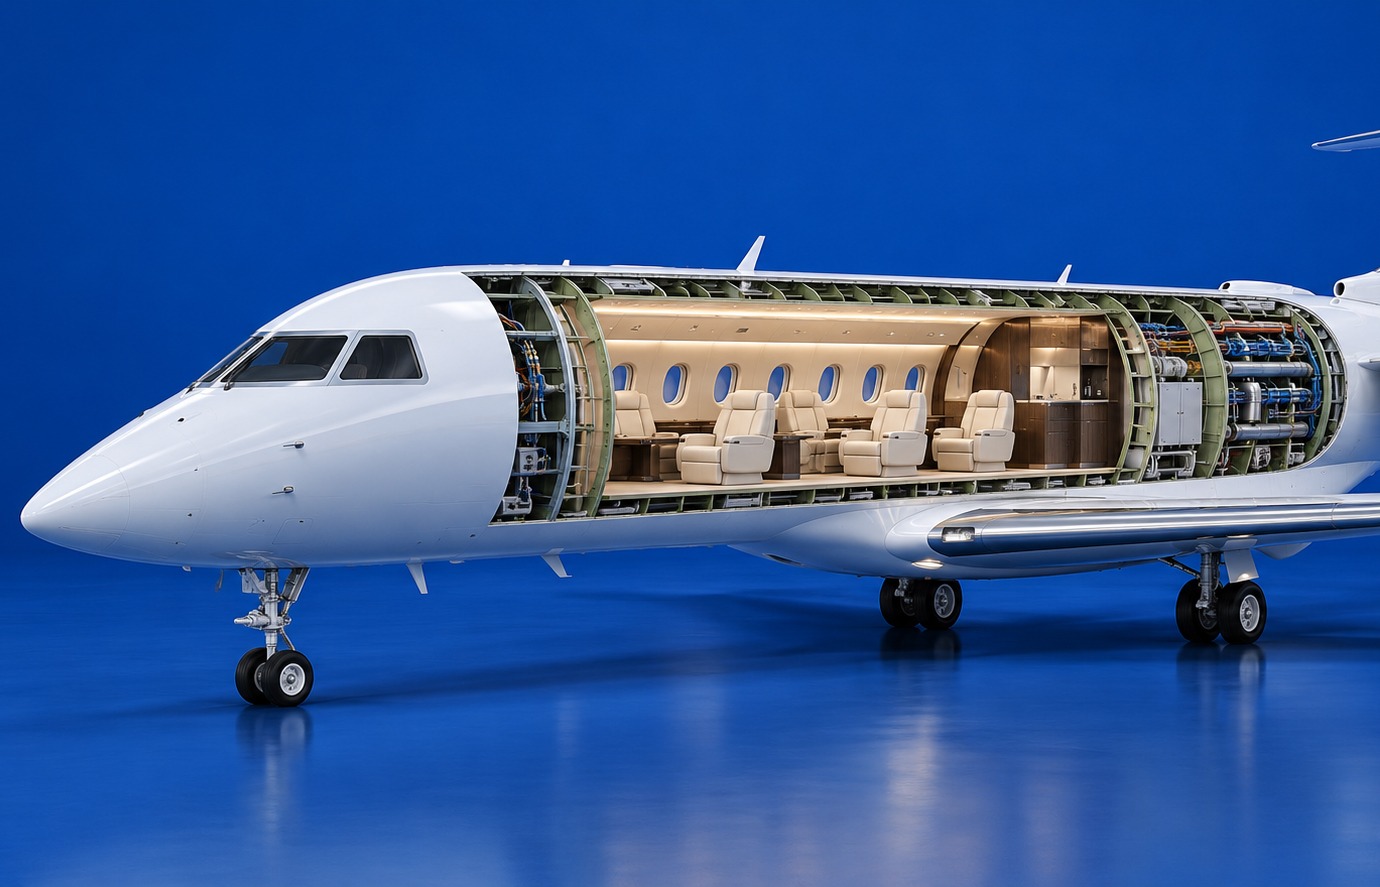
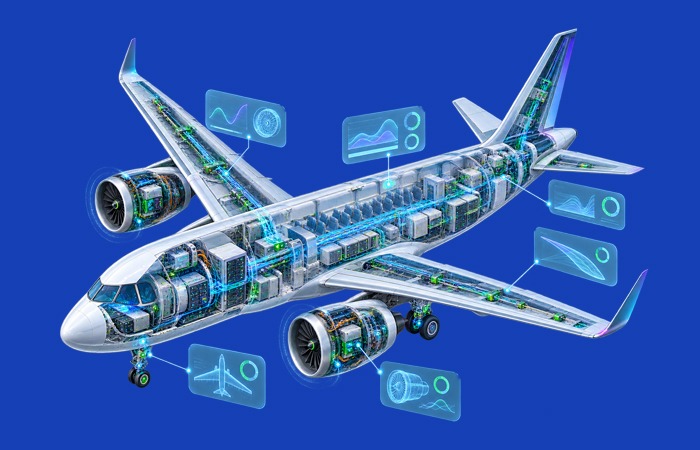
Aircraft embedded systems combine dedicated computing hardware, software, and interfaces to perform defined functions. They operate within physical systems, receiving sensor data, processing commands, and communicating with actuators or other equipment.
Applications include flight control computers, engine controllers, navigation equipment, electrical power management, environmental control, and equipment health monitoring. These functions have different safety consequences and assurance requirements. A cabin convenience function and a primary flight control function cannot be developed against the same assumptions.
For avionics embedded systems, the sensor, software, communication link, and actuator form a connected chain. Each must perform within the conditions assumed by the others.
- Flight Control Depends on Predictable Response
In fly-by-wire aircraft, computers process pilot or autopilot inputs and send electrical commands to flight control actuators. Airbus explains that flight envelope protections are embedded in the control laws and help keep the aircraft within defined operating limits. The available protections depend on the control mode and aircraft configuration.
Flight control embedded systems can support consistent handling and protection against excessive commands. Their effectiveness depends on the quality of sensor inputs, the control logic, and the timing of the complete response.
Consider what happens when two sensors disagree. The system must determine which inputs remain usable, whether its control mode should change, and what information the crew needs. An additional sensor provides value when the architecture can use it to identify and manage the disagreement.
Aircraft control systems therefore need explicit requirements for data validity, response deadlines, mode transitions, and degraded operation. These requirements should be established before software implementation begins.
- Engine Control Connects Performance with Protection
Full Authority Digital Engine Control, or FADEC, provides a practical example of embedded control. Safran describes its FADEC equipment as monitoring, protecting, and controlling propulsion in real time. It reports more than one billion accumulated flight hours across its FADEC range.
Engine controllers process operating inputs and adjust commands within the engine’s approved limits. This supports repeatable engine operation as flight conditions change and reduces the crew’s engine-management workload.
The performance benefit comes from matching control commands to changing operating conditions while protecting the engine. Any fuel-efficiency improvement must be measured against a defined engine configuration and operating baseline, since aerodynamics, propulsion hardware, and operating procedures also influence aircraft fuel burn.
Aerospace embedded systems design should therefore begin with a measurable objective, such as a specified response to changing demand or improved fault detection. That objective gives the team something concrete to verify.
- Integrated Avionics Can Reduce Hardware and Maintenance Burden
Hosting several functions on a shared computing platform can reduce duplicated equipment and simplify parts of the aircraft architecture. Airbus describes the A350 architecture as covering more than 40 avionics functions, alongside electrical networks and hydraulic circuits. It associates its simplified systems architecture with lower weight, improved dispatch reliability, fewer parts, and easier maintenance.
For other aircraft programs, similar benefits depend on which equipment can be consolidated and how the resulting dependencies are managed.
Shared platforms introduce dependencies. Functions may compete for processing time, memory access, or communication resources. A change to one application can affect the conditions under which another executes.
The FAA’s AC 20-193 addresses multi-core processors and warns that interference between software tasks can prevent safety-critical functions from completing in time. Its guidance addresses how applicable airborne systems manage these resource and timing risks.
Avionics system design must therefore assess resource use under the intended integrated workload. Average processor utilization is insufficient if a critical task misses its deadline during a demanding operating condition.
- Reliability Requires Fault Containment and Useful Diagnostics
Redundancy can improve availability when the architecture provides appropriate independence and fault handling. Two channels sharing a vulnerable power source or the same erroneous input may fail together.
Aircraft embedded system design should address:
- Which faults the system can detect and isolate.
- Which functions remain available after a failure.
- How shared power, data, and computing resources affect independence.
- What evidence supports recovery and degraded operation.
Diagnostics also affect maintenance decisions. An alert that identifies a likely failing component can help maintenance teams plan an intervention. An ambiguous alert can trigger repeated troubleshooting or an unnecessary replacement.
For aircraft electronics systems, diagnostic accuracy affects the cost and speed of fault resolution. Teams need to measure false alerts and repeat defects alongside equipment failure rates. Safety assessment must also address hazardous failure conditions independently of improvements in dispatch reliability.
- Onboard Data Makes Predictive Maintenance Possible
Embedded equipment can capture operating parameters and fault information that support maintenance analysis. Airbus’s 2018 announcement of its easyJet agreement reported that FOMAX collected 60 times more data than the existing systems used for that comparison. The agreement followed trials supporting component replacement before faults occurred.
The example shows how onboard data acquisition can support earlier maintenance intervention. Embedded equipment supplies the observations; Skywise’s ground-based analysis helps maintenance teams interpret them and decide when to act.
More recorded parameters create value when engineers can interpret them consistently. Timestamps, units, equipment identity, configuration, and operating context all matter. A trend caused by a software revision should not be mistaken for physical deterioration.
Teams should evaluate warning lead time, false-positive rates, and confirmed maintenance findings. Data volume alone does not establish a reliability improvement.
- Development Assurance Must Shape the Engineering Plan
Software and hardware assurance affect architecture, verification effort, and the evidence available for approval.
FAA AC 20-115D recognizes DO-178C and associated documents as an acceptable means of demonstrating compliance for airborne software. AC 20-152A provides development-assurance guidance for airborne electronic hardware, including recognition of DO-254. These advisory circulars describe acceptable means of compliance; they are not regulations themselves.
For the engineering team, this means maintaining a clear connection between each requirement, its implementation, and the evidence used to verify it. Leaving that work until the end can expose missing tests or undocumented design decisions after the equipment is already built.
For aircraft system integration, reviews should examine interface behavior as well as individual component performance. Verification should include invalid inputs, communication interruptions, resets, demanding workloads, and relevant failure scenarios. The exact test methods and evidence depend on the function and agreed certification approach.
What Engineering Leaders Should Measure
Programs need measures that connect embedded development to aircraft outcomes. A useful set includes control-response timing under defined workloads, resource margins, diagnostic accuracy, recovery behavior, and configuration traceability.
Operational measures can include technical dispatch reliability, repeat defects, and unnecessary component removals. Each needs a defined baseline and operating context before teams attribute improvement to an embedded-system change.
When selecting embedded systems engineering services, leaders should establish who owns the interfaces, integrated verification, and assurance evidence. Dividing hardware, software, and testing among suppliers creates a coordination responsibility that must be assigned explicitly.
How TAAL Tech Supports Aerospace Engineering Programs
At TAAL Tech, we support aerospace programs across design, analysis, verification, and technical documentation. Our capabilities include aircraft structures and interiors, installation design, stress substantiation, configuration-controlled drawing updates, and technical publications. We also provide embedded engineering services and IoT solutions within our broader engineering portfolio.
These disciplines matter when aircraft electronics must fit within existing structural, installation, and maintenance constraints. Through our aerospace engineering design services, we help customers address the physical interfaces and engineering documentation that accompany aircraft changes.
For engineering leaders evaluating embedded systems for aircraft performance, the priority is to connect the intended improvement with the work needed to prove it. A flight control function must meet its response requirements. A diagnostic function must distinguish a genuine fault from an unreliable input. An integrated platform must preserve those behaviors when other applications are running.
That is where embedded engineering delivers lasting value: in aircraft functions whose performance is demonstrated, whose failures are understood, and whose behavior remains predictable throughout service.